Modern security operations centers (SOCs) face an ongoing pipeline dilemma. While ingesting comprehensive endpoint telemetry is non-negotiable for defense, conventional delivery paths often drive up transfer overhead and alert latency. As attackers operate at machine speed, any unnecessary friction in how data moves from endpoints to the SOC can leave teams without the insight they need to respond to attacks in real time.
Addressing this requires optimizing the data pipeline at the integration layer. Rather than routing telemetry through complex intermediary cloud buckets that require ongoing maintenance and introduce costly processing delays, engineering teams need a streamlined delivery architecture. By eliminating architectural bottlenecks and optimizing data transit, security operations and IT leaders can significantly compress ingest latency, lower operational overhead, and give analysts near-instant visibility where it matters most.
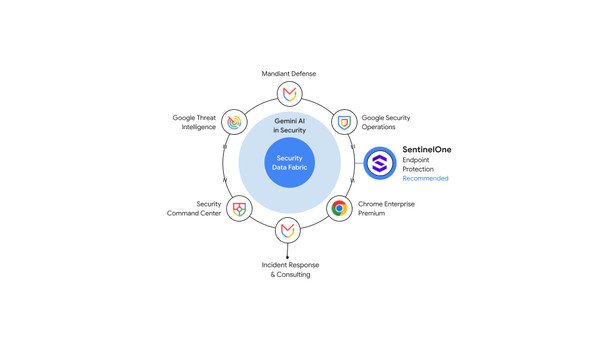
Google Cloud and SentinelOne collaborated to solve this scaling challenge with a fundamentally re-architected integration. As a Google Unified Security Recommended endpoint detection and response (EDR) partner, SentinelOne pairs with Google Security Operations through direct integration and streamlined data schemas, delivering essential endpoint telemetry visibility to Google Security Operations detection and agentic SOC pipelines while significantly reducing the total cost of ownership of the integration.
What’s at stake?
For enterprise customers, every minute of telemetry latency can increase the blast radius of an active intrusion. When detection pipelines take half an hour to surface adversary activity, incident response transitions from active mitigation to retrospective damage control.
For the broader security community and IT leadership, inefficient ingestion pipelines can impact budget and compute resources. Retaining bulky, unoptimized telemetry in intermediate staging environments diverts resources away from strategic security initiatives and saddles engineering teams with unneeded infrastructure debt.
Technical highlights and capabilities
The re-engineered integration between Google Cloud and SentinelOne introduces six dedicated engineering workstreams designed to remove ingestion bottlenecks and reduce data overhead without sacrificing detection fidelity:
-
Significant event size reduction: A modernized EDR data schema greatly reduces the average event size, preserving full analytical fidelity and reducing downstream compute load for agentic workflows.
-
Direct Google API ingestion: SentinelOne directly streams events into Google Security Operations with APIs, eliminating intermediate cloud storage hops and associated storage fees.
-
Reduced streaming latency: Removing the requirement for intermediate cloud storage makes data available for detection, investigative, and agentic workflows in Google Security Operations in near real-time.
-
Precision telemetry scoping: Integrated SentinelOne Cloud Funnel filters allow further flexibility to customize telemetry sent to Google Security Operations.
-
Unified alerts API and Mandiant alignment: Parsers, alert models, and SOAR playbooks were engineered alongside Mandiant Incident Response and Managed Defense teams to support automated host isolation, full-disk deep visibility scans, malware extraction, and artifact enrichment directly from Google Security Operations.
-
Industry-validated partnership: Named Google Threat Intelligence’s Intel Partner of the Year at Google Cloud Next.
Transform your SOC ingestion today
Modern defense requires direct action, not delayed transit. By cutting out unnecessary staging layers and streaming directly via APIs, your security team gains the speed needed to outpace modern threats while protecting your budget.
Targeted for phased delivery by end of year, initial rollouts are prioritizing customers using Mandiant Managed Defense and Mandiant Threat Defense. Contact your Google Cloud or SentinelOne account team today to evaluate your current telemetry pipeline, schedule a technical architecture review, and reserve early access for your environment.